Know what your software
is made of.
Light Squares secures your software supply chain. We proactively audit every dependency update, prove every build, and show you what to fix first.
You can check the evidence behind every result yourself.
Software supply chains are increasingly complex and under attack
from third-party dependencies to trusted servers. AI makes everything faster.
- crates.io
- npm
- PyPI
- Maven
- NuGet
Backdoored or unaudited updates can introduce malicious code.
Source
- Unauthorised change
- Hijacked source repository
Build
- Built from other source
- Tampered build server
Consumer
- Untrusted software
- Unverifiable provenance
Source
- Unauthorised change
- Hijacked source repository
Dependencies
- Backdoored or unaudited updates can introduce malicious code
- crates.io
- npm
- PyPI
- Maven
- NuGet
Build
- Built from other source
- Tampered build server
Consumer
- Untrusted software
- Unverifiable provenance
See who you depend on, audit what changes, prove how it's built.
see Supply Chain Intelligence across the whole chain
- crates.io
- npm
- PyPI
- Maven
- NuGet
audit Dependency Canary audits every update before it reaches your build.
Source
Consumer
Source
Dependencies
- crates.io
- npm
- PyPI
- Maven
- NuGet
Consumer
Software Supply Chain Intelligence
Know which suppliers and packages need your attention, and turn your due diligence into evidence for CRA and NIS2.
Become a design partner →Dependency Canary
An AI audits your dependency updates proactively before they run in your infrastructure or ship to your customers.
- Live Public feed, cargo-vet import
Attestable Builds
Run your existing builds in a hardware-protected environment that provides verifiable source-to-artifact provenance.
Learn more →Dependency CanaryPublic preview
Every dependency update, read before you ship.
A typical Rust project pulls in 8,700 changed lines of dependency code a week. Dependency Canary audits them with AI and publishes the results as a free cargo-vet feed, so your team gets that review time back. It covers Rust today, with .NET / NuGet next and then Java / Maven.
Learn more →Set it up with your coding agent
Claude Code, Codex or any agent that reads a URL.
Add the Dependency Canary audits to this project using the skill at https://github.com/lightsquares/skills/blob/main/lightsquares-dependency-canary/SKILL.mdAs of 23 September 2026.
What does auditing every update cost you?
Move the slider to match your project. The numbers come from a year of real dependency updates in Rust projects that use cargo-vet.
Includes direct and transitive dependencies.
5.1
dependency updates a week
8,700
changed lines to review a week
Auditing every update yourself costs
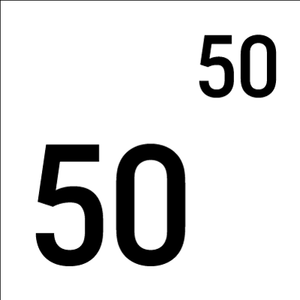
£50,000
a year in engineering salary
910
engineering hours a year
0.5
full-time engineers auditing diffs
Update rates are per-dependency medians across 128 Rust projects over the 12 months to July 2026, from our cargo-vet study. Assumes a quick review pace of 500 changed lines an hour (careful review is usually put at 200 to 400) and the median London software engineer salary of £95,000 (ITJobsWatch, January 2026) over 1,725 working hours a year, before employer costs.
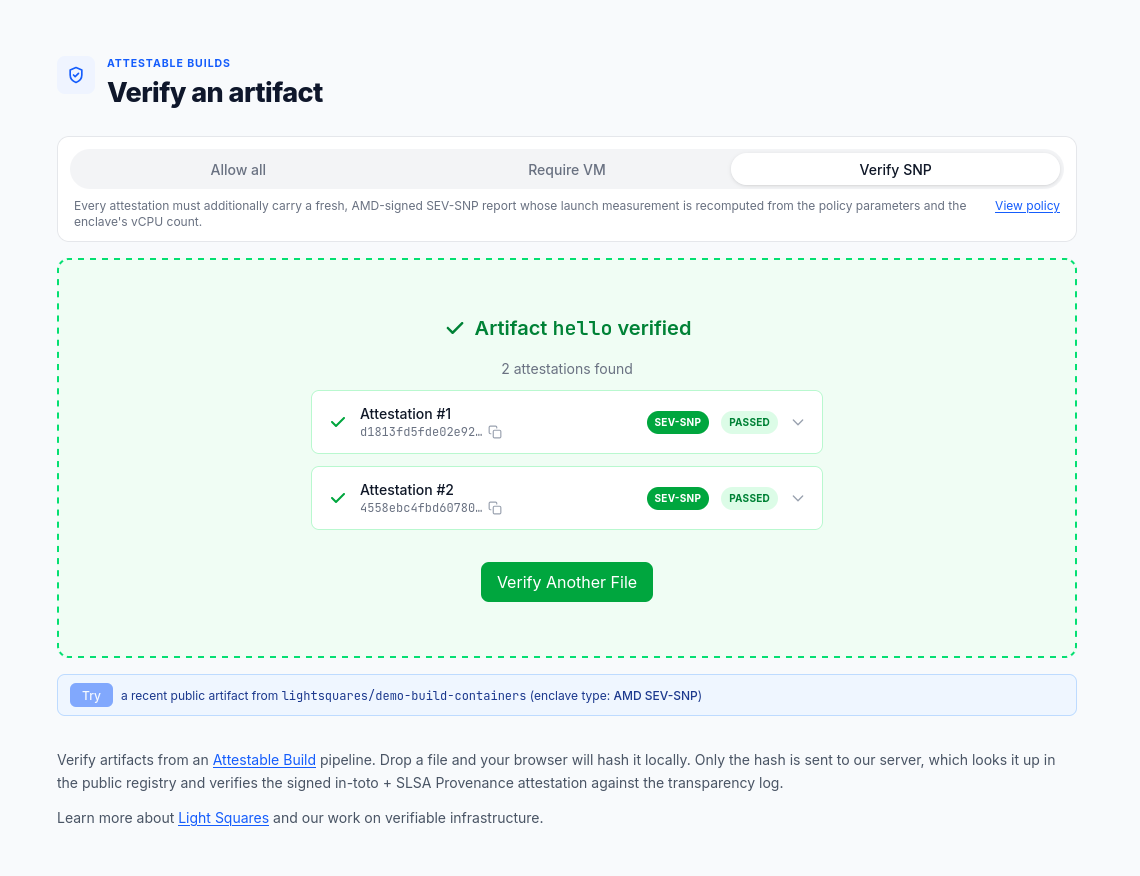
Attestable BuildsEarly access
Prove every build, and let anyone check.
Run your existing build in a hardware-protected environment. The verifiable evidence proves to everyone that the artifact was built correctly from the source code. Ensure sovereignty and zero-trust in your build infrastructure.
Set it up with your coding agent
Claude Code, Codex or any agent that reads a URL.
Add Attestable Builds to this project using the skill at https://github.com/lightsquares/skills/blob/main/lightsquares-attestable-builds/SKILL.mdSoftware Supply Chain IntelligenceDesign partners
Focus on what matters most in your supply chain.
Software Supply Chain Intelligence shows you the suppliers and packages behind your products and how much you can trust each one, using the evidence from Canary audits and Attestable Builds. You see where to act first, and your due diligence for CRA and NIS2 builds up as you work.
Suppliers & open-source dependencies
Built by researchers.
Daniel Hugenroth and Mario Lins met at the University of Cambridge during their PhDs, working on systems security and software supply chains. Light Squares turns that research into products, built in Europe, and is part of the ARIA-funded Centre for Cryptographic Trust Infrastructure.

Daniel Hugenroth
Co-Founder
PhD, University of Cambridge. Systems security, applied cryptography, and confidential computing.

Mario Lins
Co-Founder
PhD, JKU Linz; visiting researcher at the University of Cambridge. Software supply chain security and industry expert.
Selected papers
- Attestable Builds: Compiling Verifiable Binaries on Untrusted Systems using Trusted Execution Environments ACM CCS 2025
- Unveiling the Critical Attack Path for Implanting Backdoors in Supply Chains: Practical Experience from XZ CANS 2025
- Firmware Transparency: Strengthening Security Guarantees Against Bootloader-Targeting Attacks ACNS 2026
- Attestable Audits: Verifiable AI Safety Benchmarks Using Trusted Execution Environments ICML 25 TAIG Workshop
Supported by


Get ahead of your supply chain.
Start with the free Rust audits, or become a design partner: early access to what we're building and a direct line to the founders.